Agentic AI Security Buyer’s Checklist: 15 Questions to Ask Before You Sign
TL;DR Buying agentic AI security software is a fast-moving decision with high stakes. Get it wrong, and your security team ends up chasing agent activity it
TL;DR Buying agentic AI security software is a fast-moving decision with high stakes. Get it wrong, and your security team ends up chasing agent activity it
TL;DR The Confidence Trap Most security leaders believe their API attack surface is covered. A Web Application Firewall (WAF) sits in front of the application. An API gateway manages authentication, rate limiting,
TL;DR AI agents are moving fast from pilot projects to production systems. They book meetings, process refunds, query databases, and call internal APIs on their own.
TL;DR AI agents don’t just answer questions anymore. They call APIs, move data between systems, trigger workflows, and make decisions that used to require a human
TL;DR Every enterprise security leader is being asked the same question by their board: are we secure against AI risk? Most cannot answer it with confidence,
TL;DR How a Claude-Powered OpenClaw Agent Exploited a Gym API to Steal a Workout Slot An Australian man named Andrew asked his personal AI agent, built on the
TL;DR Two Second Stages, One Blind Spot Most coverage of API breaches focuses on the entry point: the poisoned package, the compromised maintainer account, the malicious
TL;DR It’s one pattern An agent reads a file, approves its own next action, and the change survives the session. That one design choice, repeated across
TL;DR Healthcare has spent years strengthening its infrastructure against ransomware, patching vulnerabilities, deploying endpoint detection, and implementing zero-trust architectures. Yet, attackers continue to find new ways to compromise healthcare organizations.
TL;DR AI Has Rewired How Healthcare Operates Healthcare has moved well past pilot projects. AI agents now triage support tickets, draft clinical documentation, manage patient engagement,
APIs power nearly every digital interaction today, from mobile banking to AI chatbots. Yet poorly secured api endpoints remain one of the fastest paths to a catastrophic breach.
TL;DR One phone call. One deceived agent. 5.7 million exposed records and zero regulatory penalty. That’s the uncomfortable arithmetic behind the Office of the Australian Information Commissioner’s July
TL;DR AI Agents Are the New Decision Layer, and Nobody Fully Sees What They’re Calling Ask any security leader how many APIs their organization runs, and you’ll usually
TL;DR The Access Problem No One Scoped Properly Model Context Protocol (MCP) is what turns an AI assistant into an AI agent. It’s the standardized bridge
TL;DR Nine seconds. One API call. A car rental software company’s production data was gone. That’s the headline from the PocketOS incident, and it’s the reason
TL;DR What Is the OWASP Top 10? OWASP, the Open Worldwide Application Security Project, has published Top 10 lists for over two decades to help security
Key Takeaways Introduction AI systems are starting to do more than generate answers. Across customer support, IT operations, software development, and internal business workflows, organizations are
Key Takeaways Agentic AI Changes What Application Security Has to Cover A human employee who wants to delete a customer record, issue a refund, or push a config change has to ask,
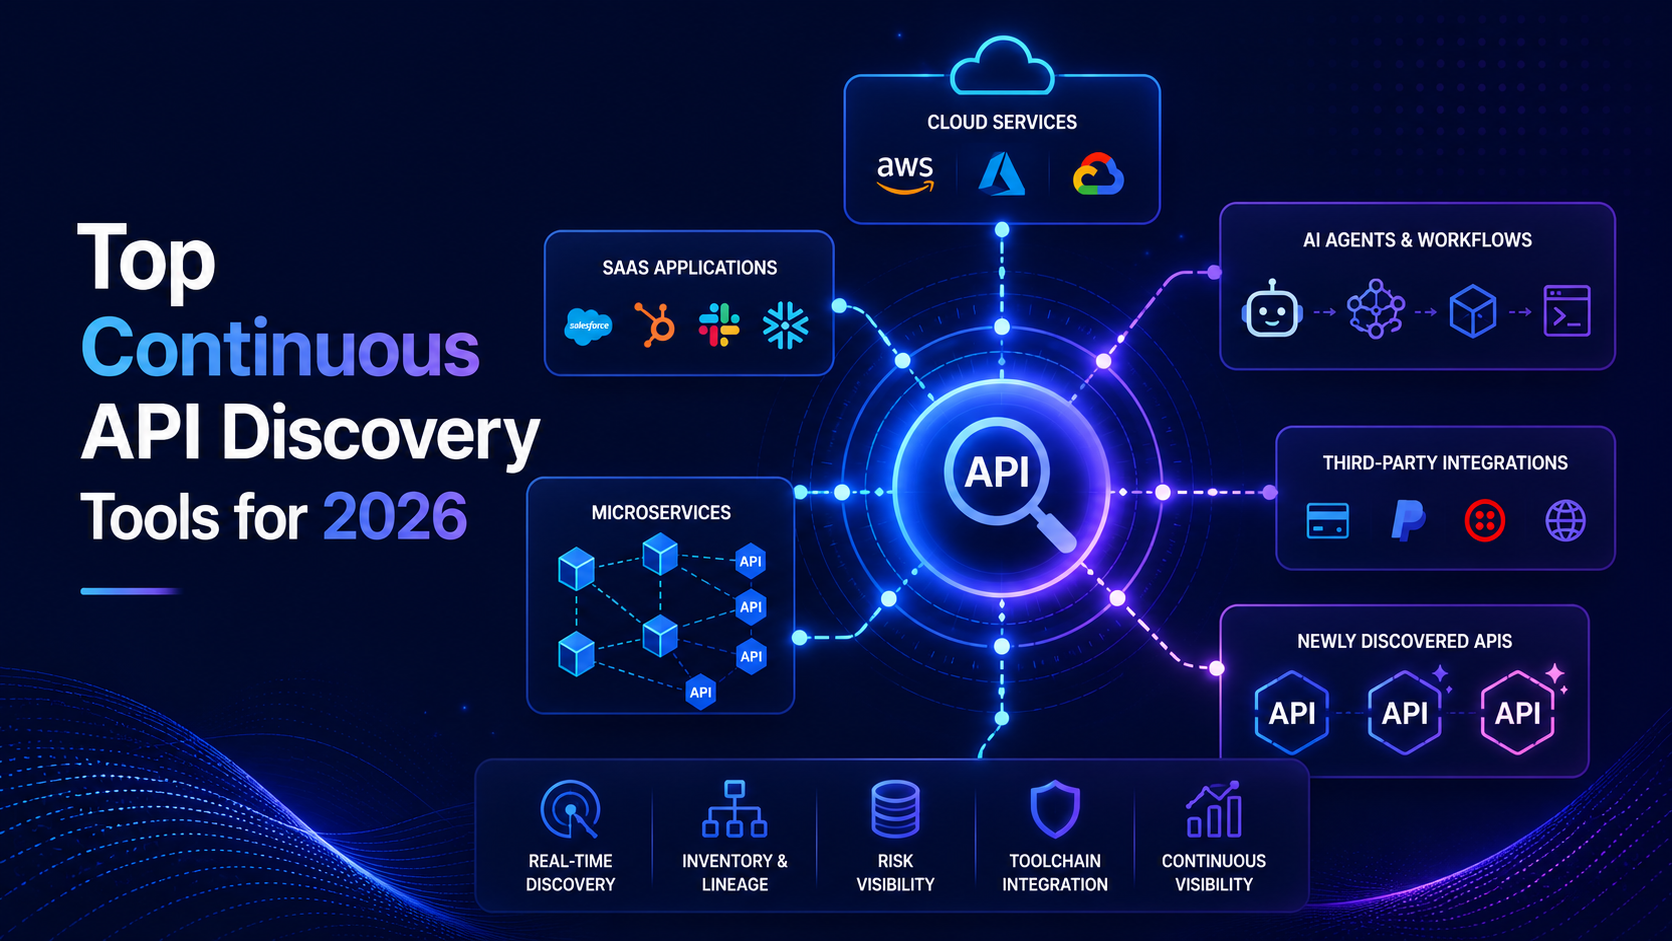
Not all API discovery tools solve the same problem. Some help teams discover APIs once.
Organizations are investing heavily in securing their AI initiatives. New governance frameworks are being established, AI usage policies are being drafted, and security teams are deploying tools that provide visibility into AI agents,
Key Takeways Your Next Fraud Incident Won’t Come From a Human An AI agent with access to a customer’s brokerage account can begin executing trades. Not because the customer asked. Because
TL;DR The Permission Inheritance Problem Nobody Is Talking About When an enterprise deploys an MCP-powered AI agent, such as a coding assistant, a customer workflow automaton, an IT
When researchers disclosed the Lovable.dev vulnerability, the headline made it sound like a sophisticated attack. It wasn’t. There was no exploit.
Key Takeaways The Moment the Internet Tipped On April 27, 2026, a threshold was crossed that the internet had never hit before. Cloudflare Radar data confirmed that automated systems,
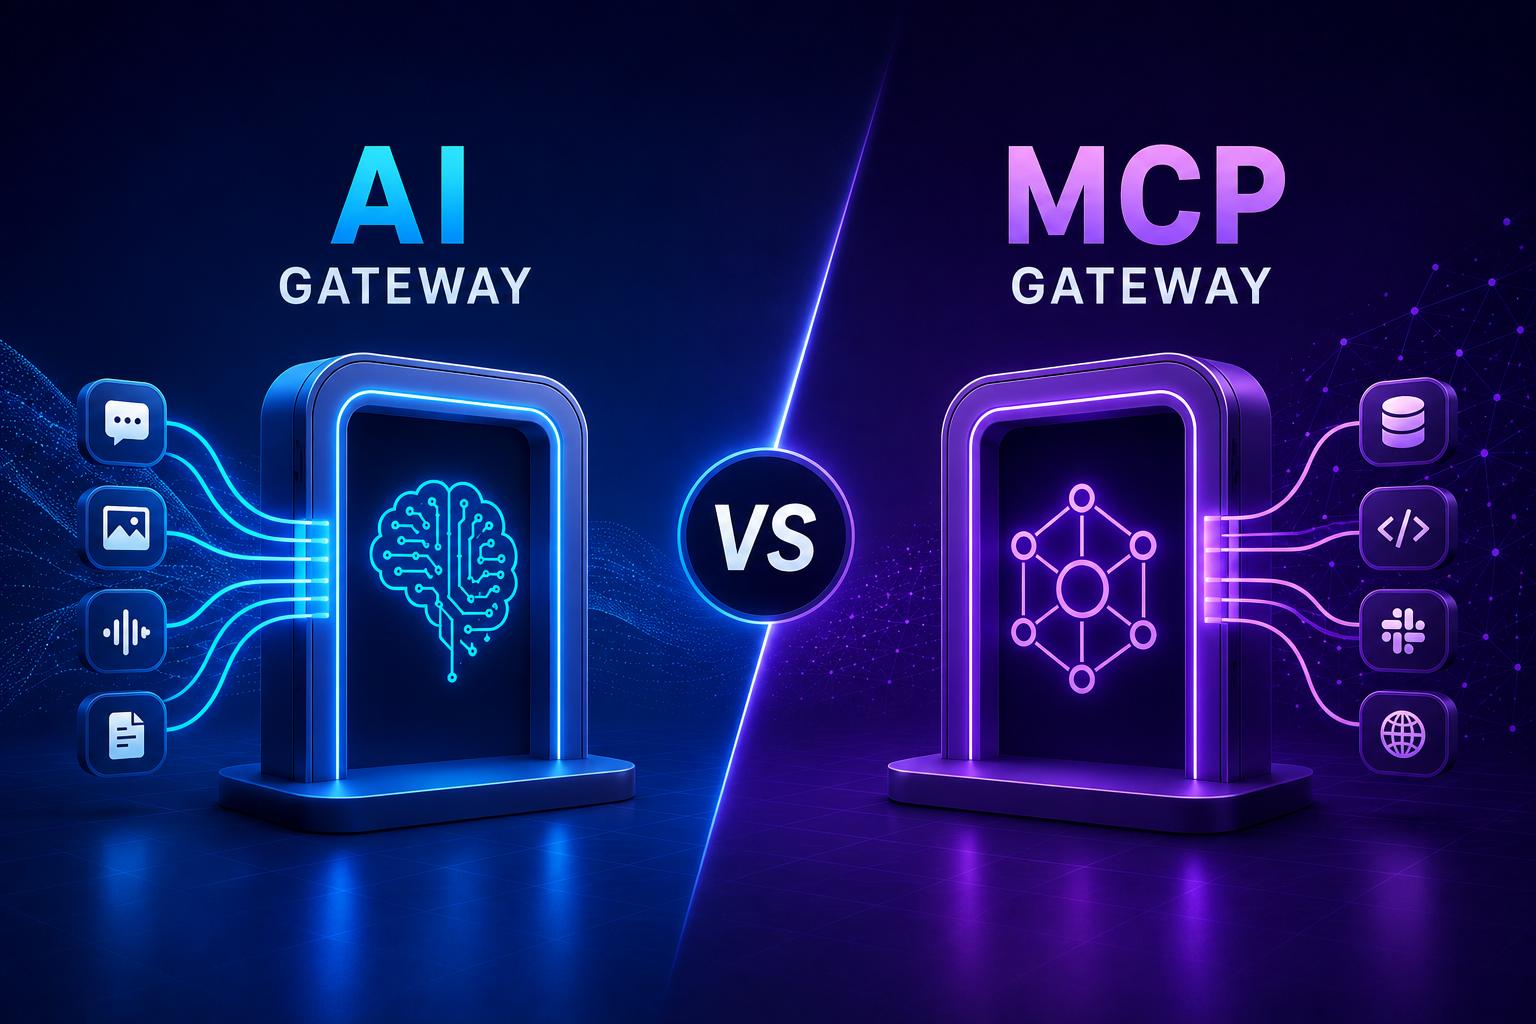
As enterprises adopt AI agents, two control points are becoming common: AI Gateways and MCP Gateways. They sound similar, but they solve different problems. An AI Gateway controls how applications interact
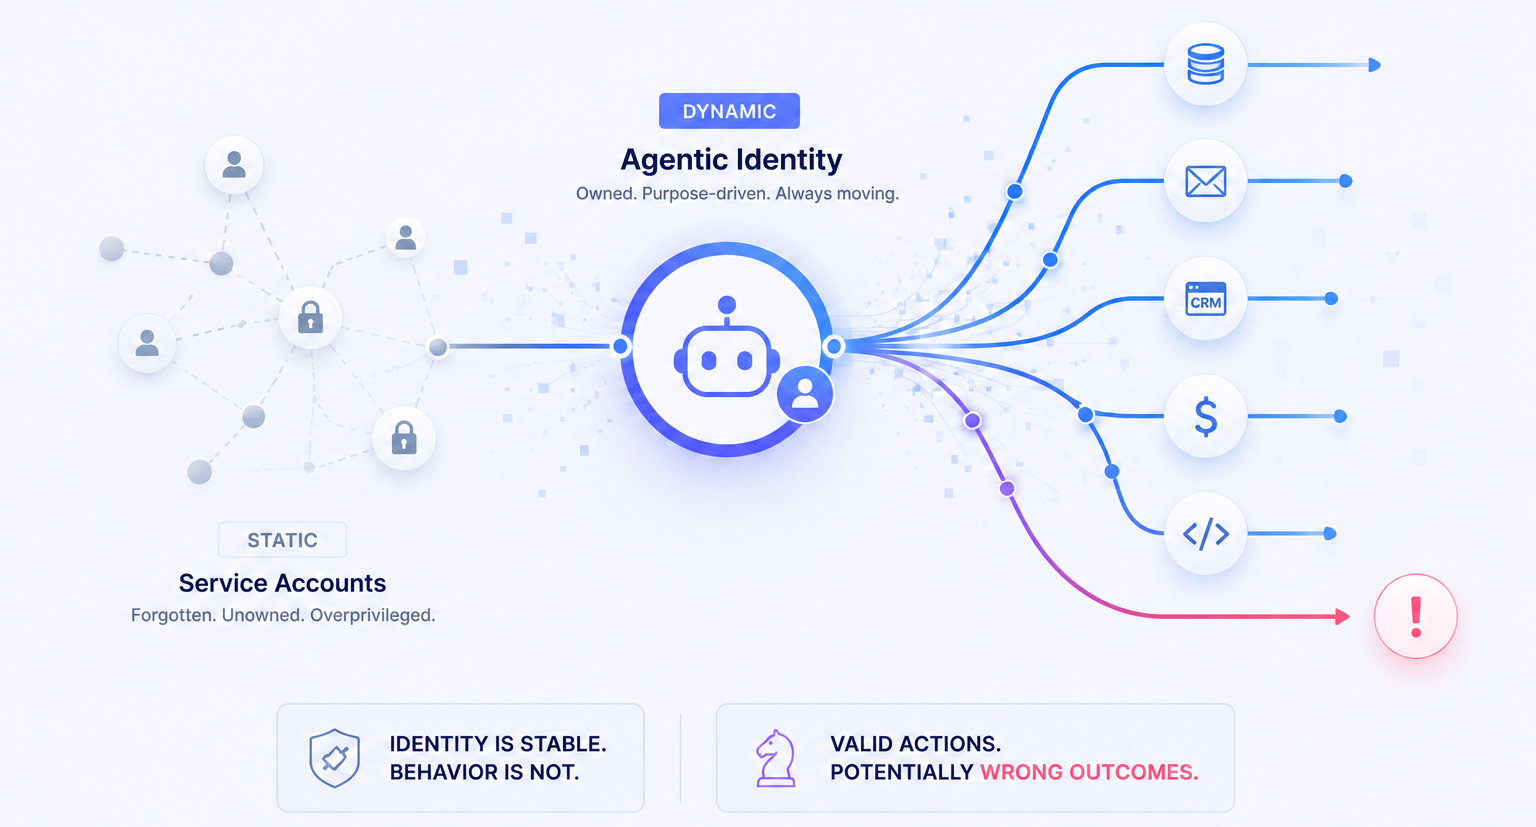
The non-human identity (NHI) problem was always the same problem: too many service accounts, too few owners, too many secrets in too many places.
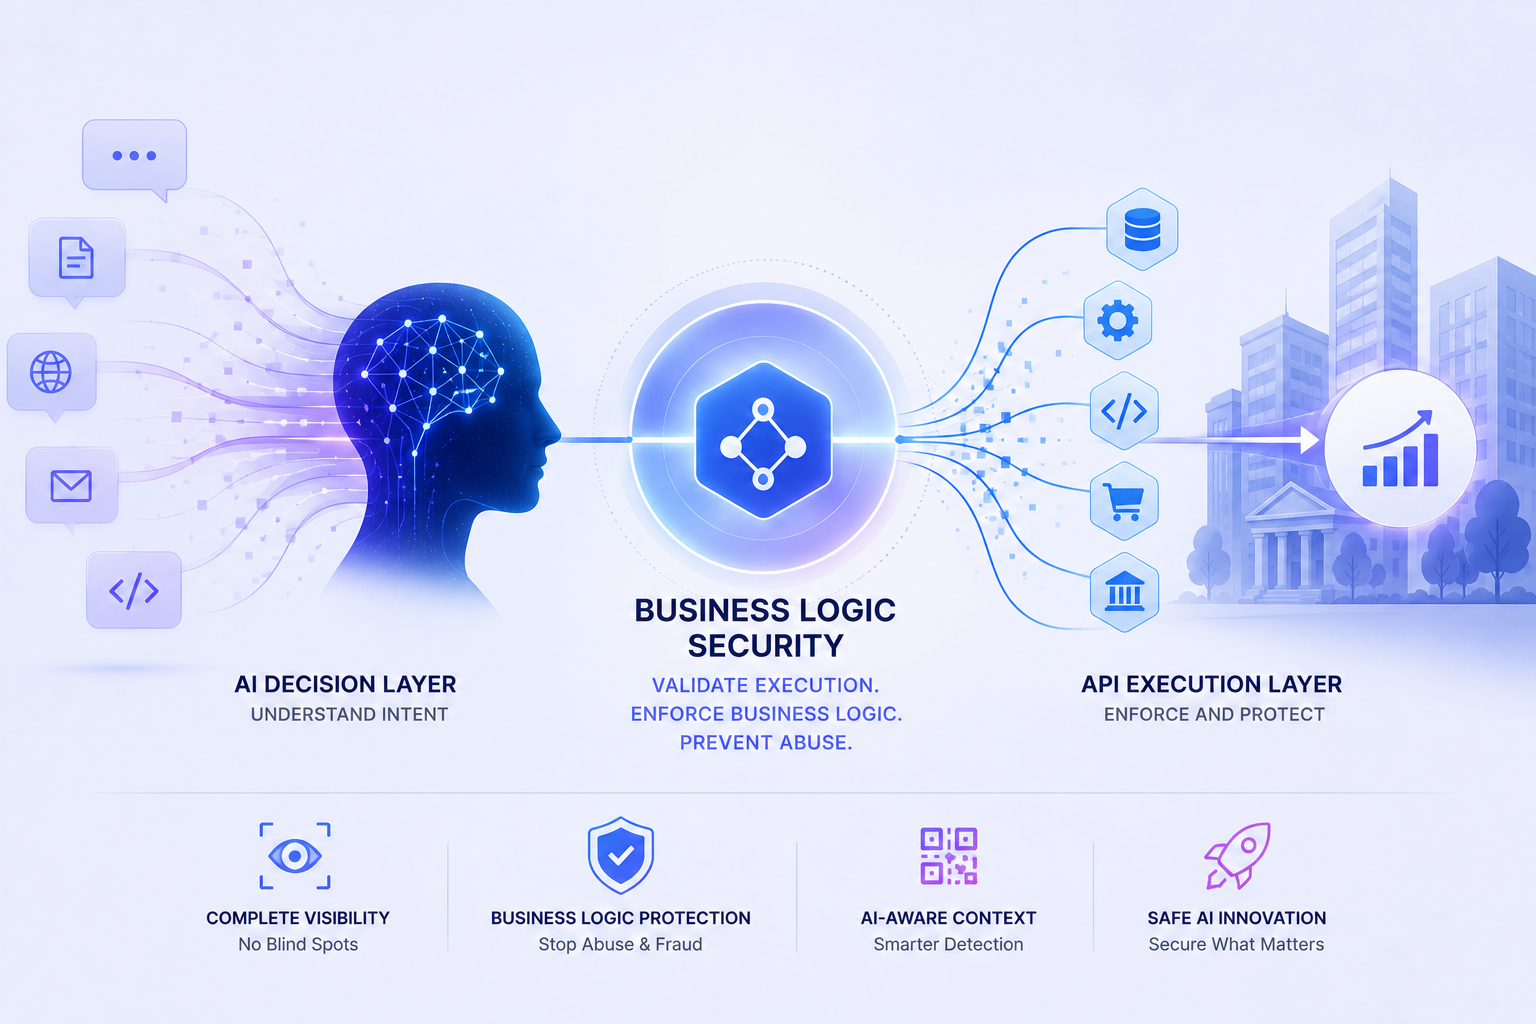
The enterprise security world is having two separate conversations that desperately need to collide. On one side, application security (AppSec) teams are scrambling to secure APIs – the connective tissue of